The Complete Corporate Cybersecurity Toolkit
One-Time Download. Perpetual Corporate Licence.
Instant download access to comprehensive, editable corporate policies, procedures, and high-impact employee training videos.
Deploy Enterprise-Grade Cyber Security Protection & Compliance in Under 24 Hours
- Save 40+ hours of agonising legal and compliance writing.
- Engaging HD Videos with practical scripts broken into bite-sized modules under 5 minutes.
- Immediate Deployment—simply preview the files below and launch your framework today.
Some common threats


Why This Toolkit is Built Differently:
User Friendly
Action Oriented
Zero Subscriptions
We have stripped away the complexity.
Download the complete asset vault once and host it entirely on your own internal systems.
- Core Benefits:
- Fully Editable Policies (.docx): A complete repository of ready-made policies to tailor cleanly to your business profile and adopt immediately.
- Step-by-Step Practical Guide: Take immediate, measurable control over your organisational cyber risk.
- Instant Audit-Ready Framework: Ready-to-use printouts and tracking matrices for your corporate compliance records.
- Bite-Sized Employee Video Assets (.mp4): No painfully long corporate compliance modules. Just punchy, 5-minute takeaways your staff can watch over their morning coffee.
- Native Communication Sharing: Drop the files directly into your existing internal Slack channels, Microsoft Teams hubs, or company intranet.
- Never Pay a Recurring Fee: One flat investment gives your organisation lifetime access with no monthly per-user costs.
PREVIEWS OF VIDEOS
Phishing
Phishing is when a user - like you - is ‘baited’ or tricked to reveal sensitive information (like usernames, password, or client data) to allow an attacker to breach the system, or steal funds and intellectual property.
Sniffing & MITM
A ‘Man in the Middle’ sniffing attack occurs when the attacker is intercepting communications between you and a legitimate service. e.g. your bank login details over the network. Attackers ‘sniff’ them out and steal them.
Malware
‘Malware’ is short for Malicious Software. It refers to software which is used to gain access to your system without you knowing it.
Compromised Credentials
The easiest way for a cyber-attacker to gain access to sensitive data is by ‘compromising’ the identity and credentials of an end user, like you. This allows them undetected access. If you are a “privileged” user with broad access, that could give out the ‘keys to the kingdom’.
Cyber Security -You're not ready
DDOS and Ransomware
Have you experienced when the online service you are trying to access is un-workably slow or even crashes. A Distributed Denial of Service attack or DDOS can achieve that outcome. “Ransomware” has 2 parts. Firstly it prevents users from accessing their system or personal files. And Secondly, it demands payment be sent by cryptocurrency or credit card.
PREVIEWS OF POLICIES
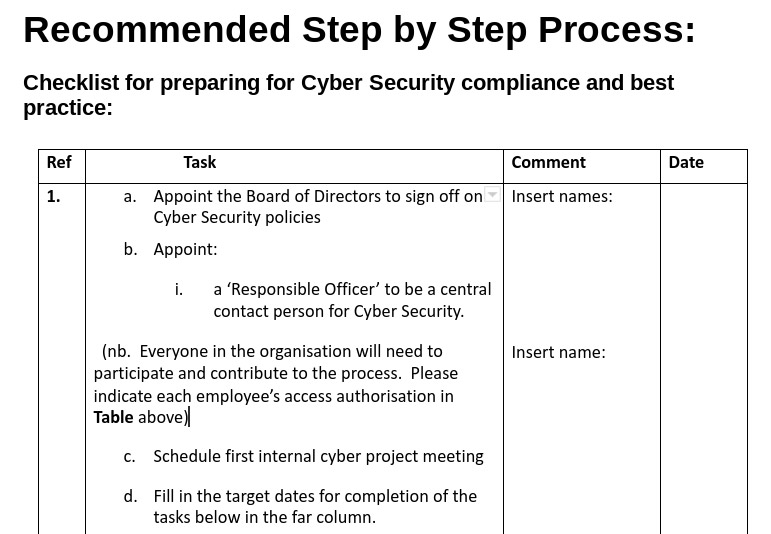
Recommended Step by Step Process
This checklist will enable you to progressively adopt all recommended procedures. It helps you to demonstrate to stakeholders and regulators you have understood the Cyber Risks requirements as they apply to you, and provides a process for on-going Cyber Security compliance.
Staff training plan
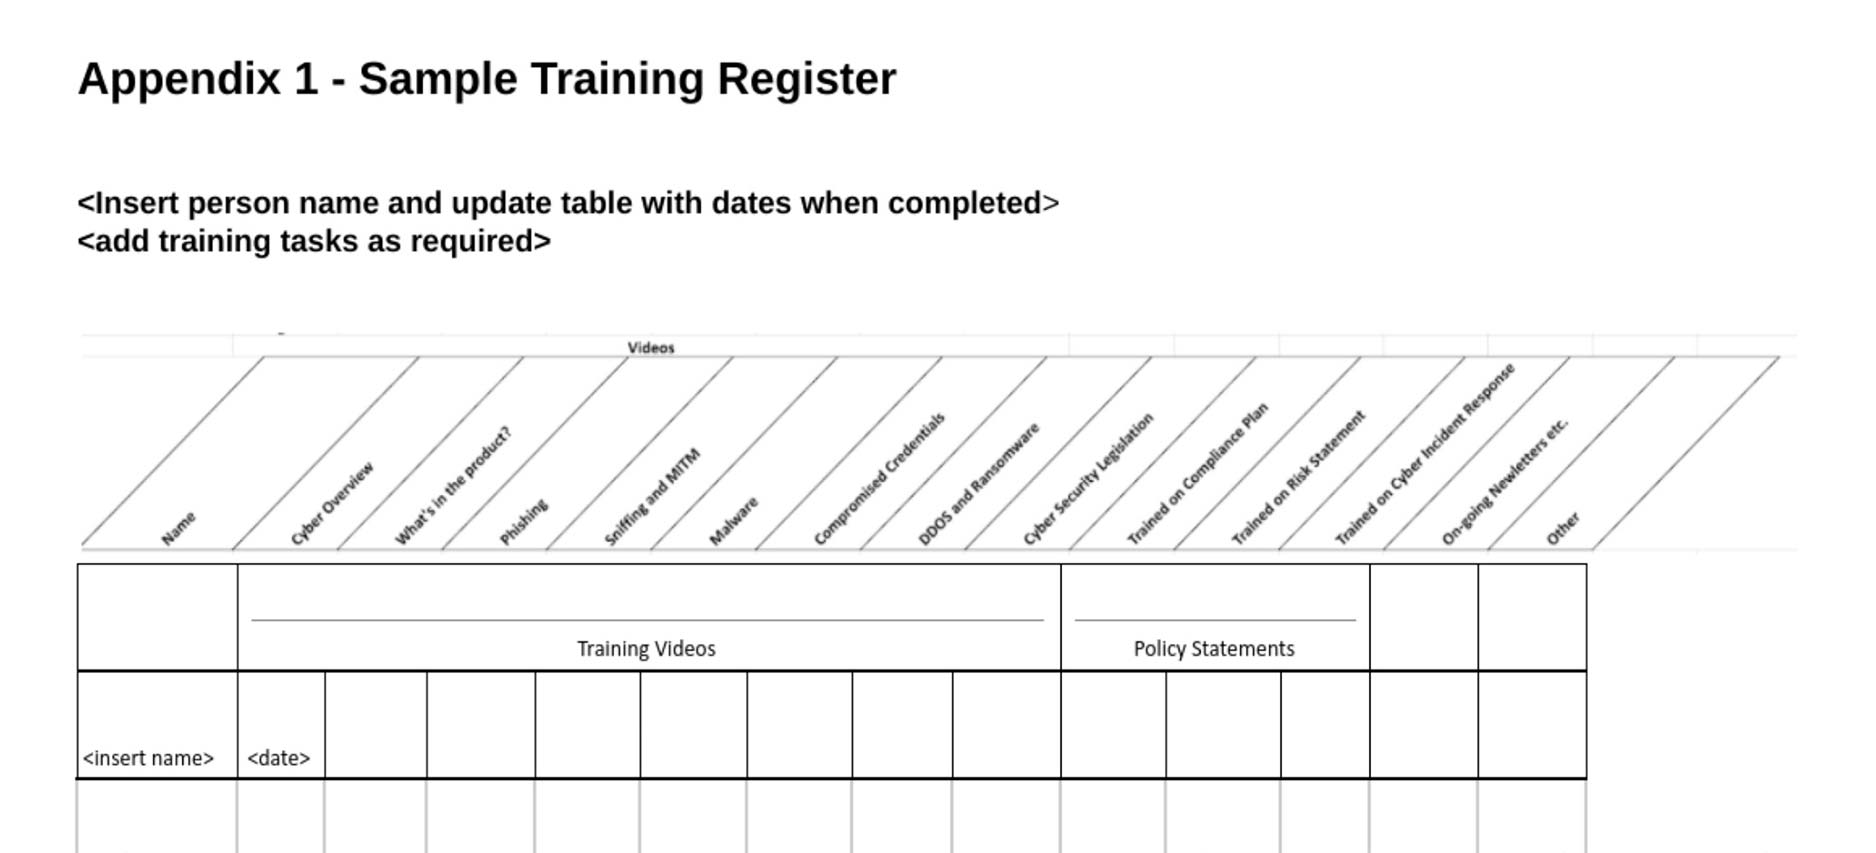
The training plan provides a structure to analyse tasks performed, consider the level of cyber training required, record & monitor.
Good practice requires cyber risk awareness training of key threats, personal, regulatory and organisational responsibility, and mitigation.
Induction of new staff procedures
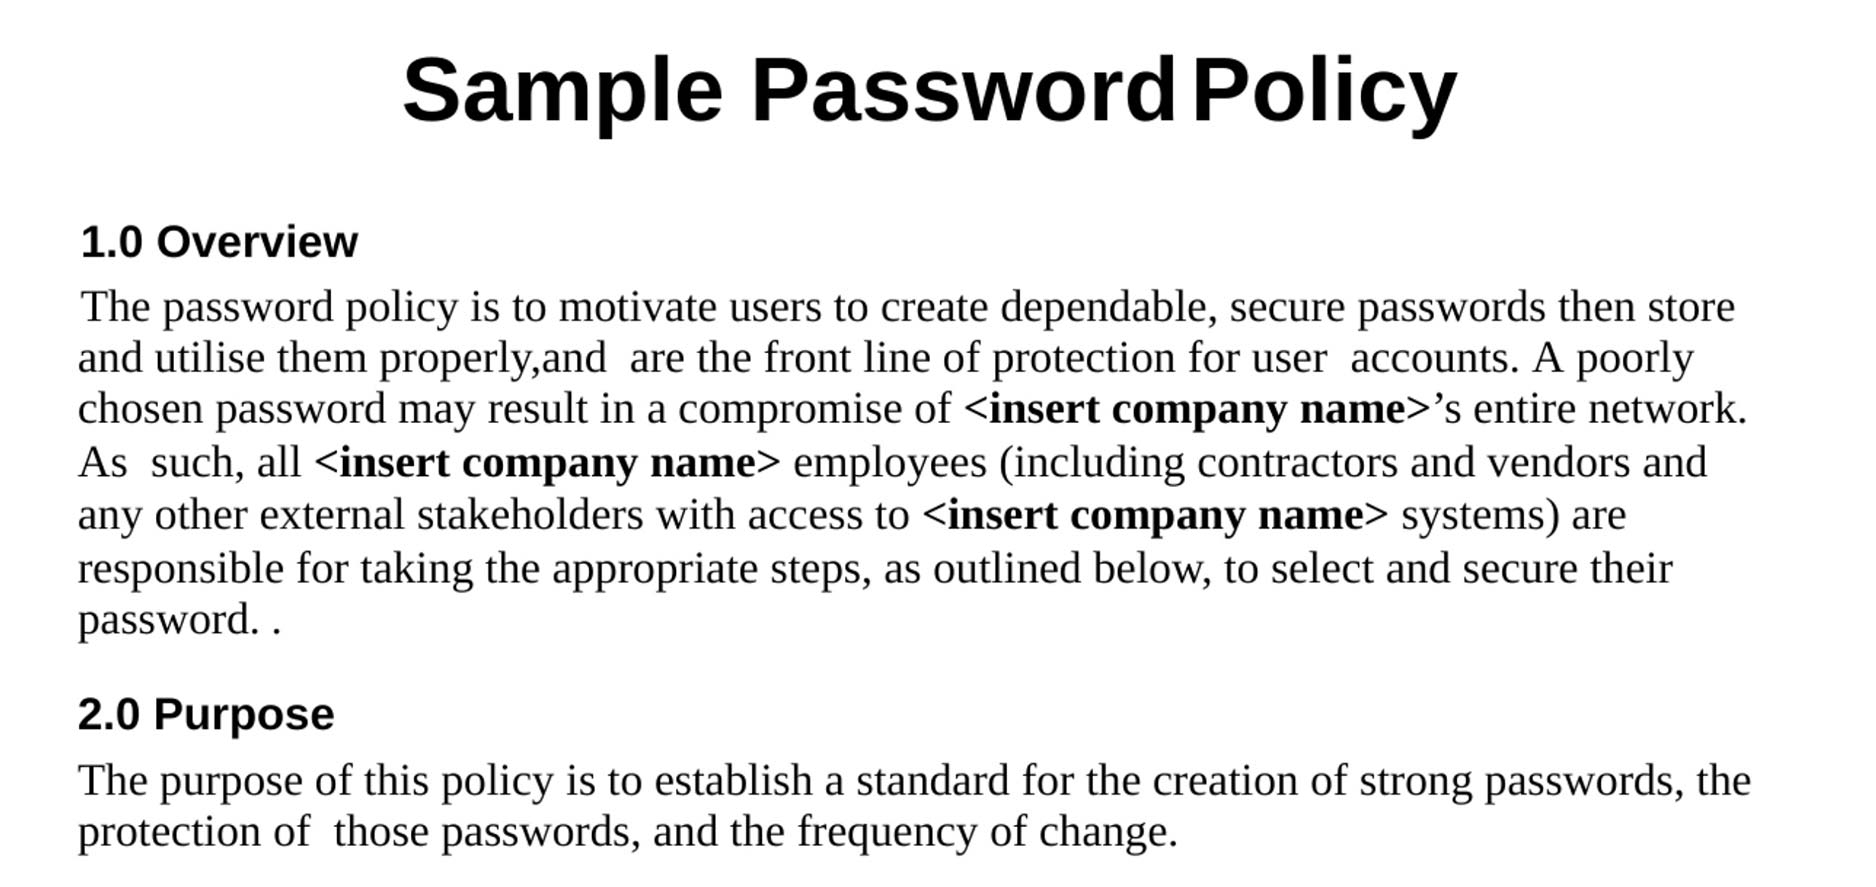
All new staff will undertake formal structured cyber induction training upon commencement, as well a continuing cyber training program. Details of induction training include keeping a register of systems accessed, issuing password policy and an acceptable use policy.
Risk management statement
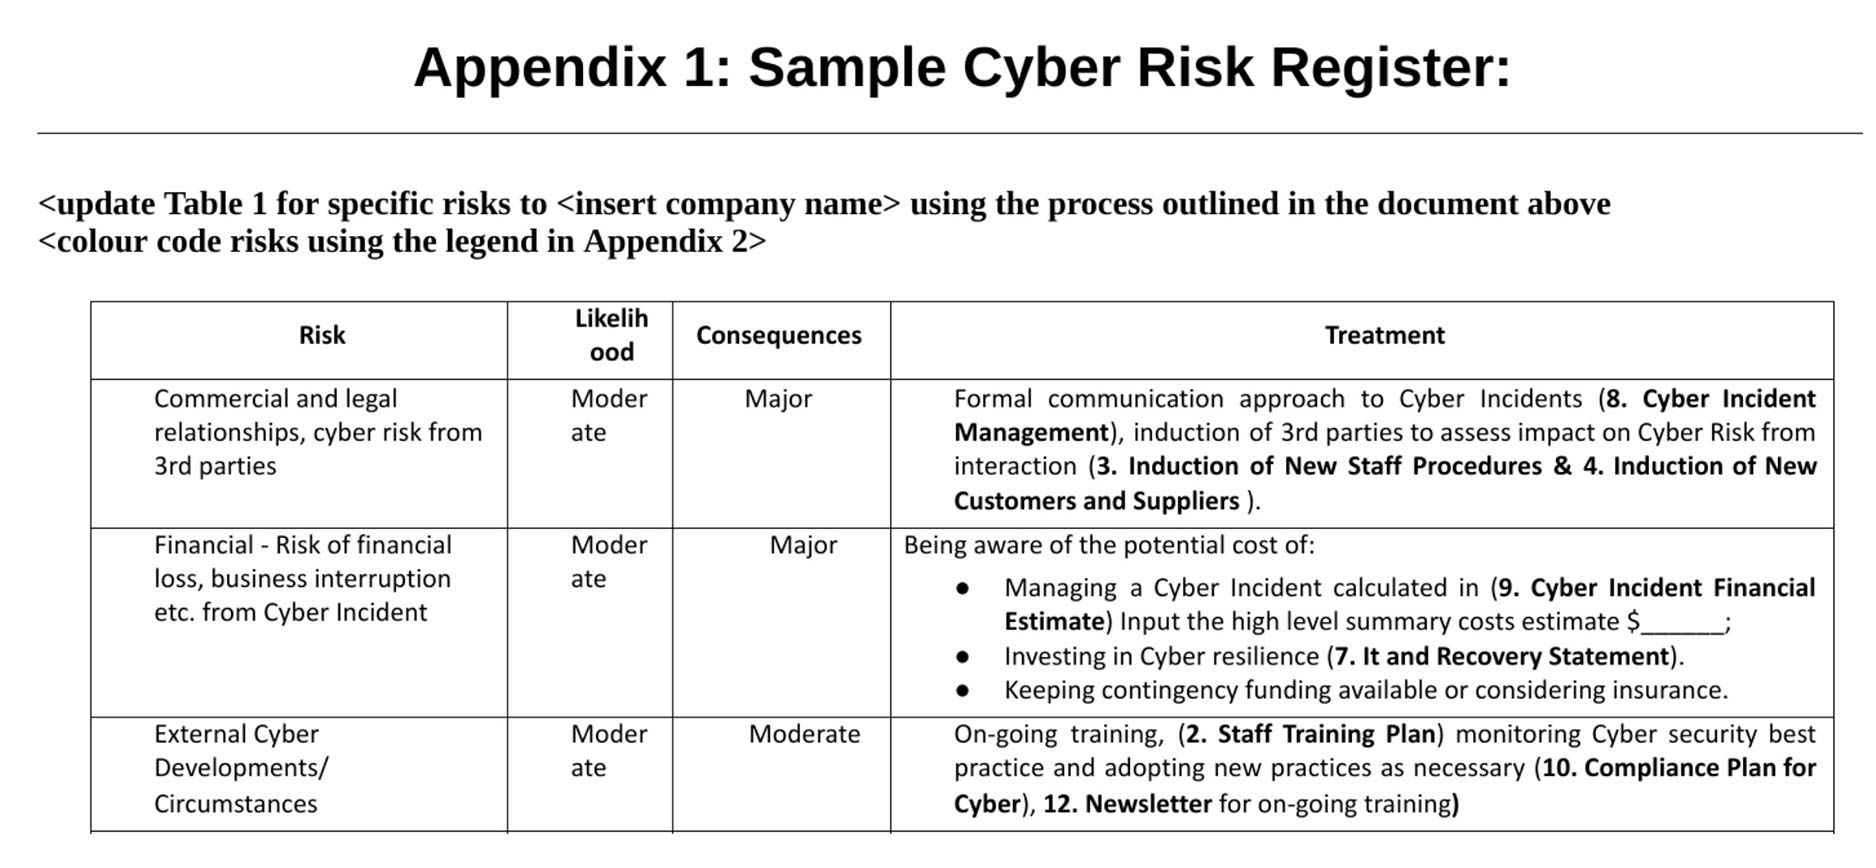
Cyber risk exposures must be recognised, and then assessed for impacts based on clearly defined metrics such as response time, cost and legal or compliance implications. A risk plan can then be developed.
Built by industry experts, designed for immediate action
IT and recovery statement
This statement aims to reduce cyber risk by identifying and maintaining systems in use, eliminating threats, scheduling and running scans, documenting backup and restore routines, and other technology security processes.
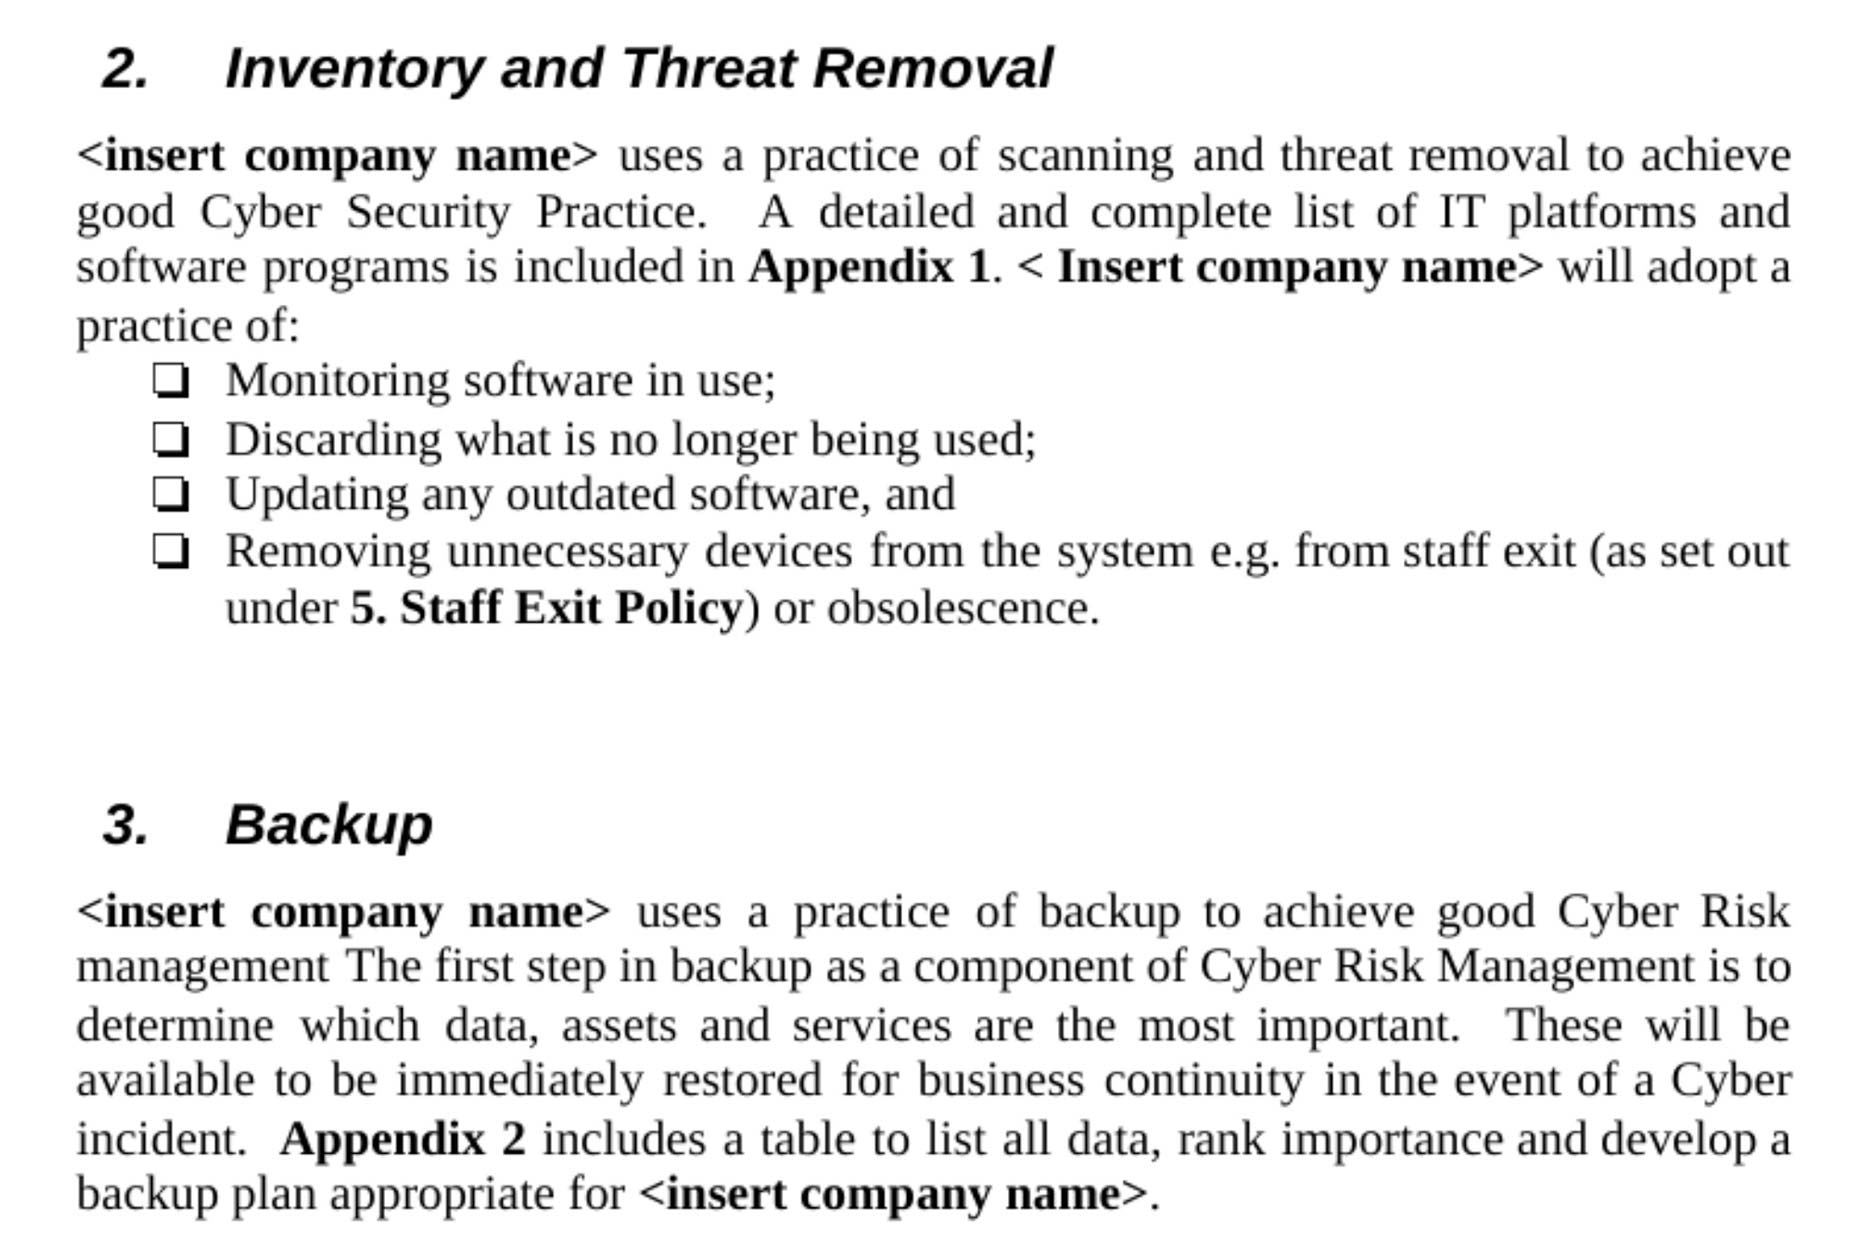
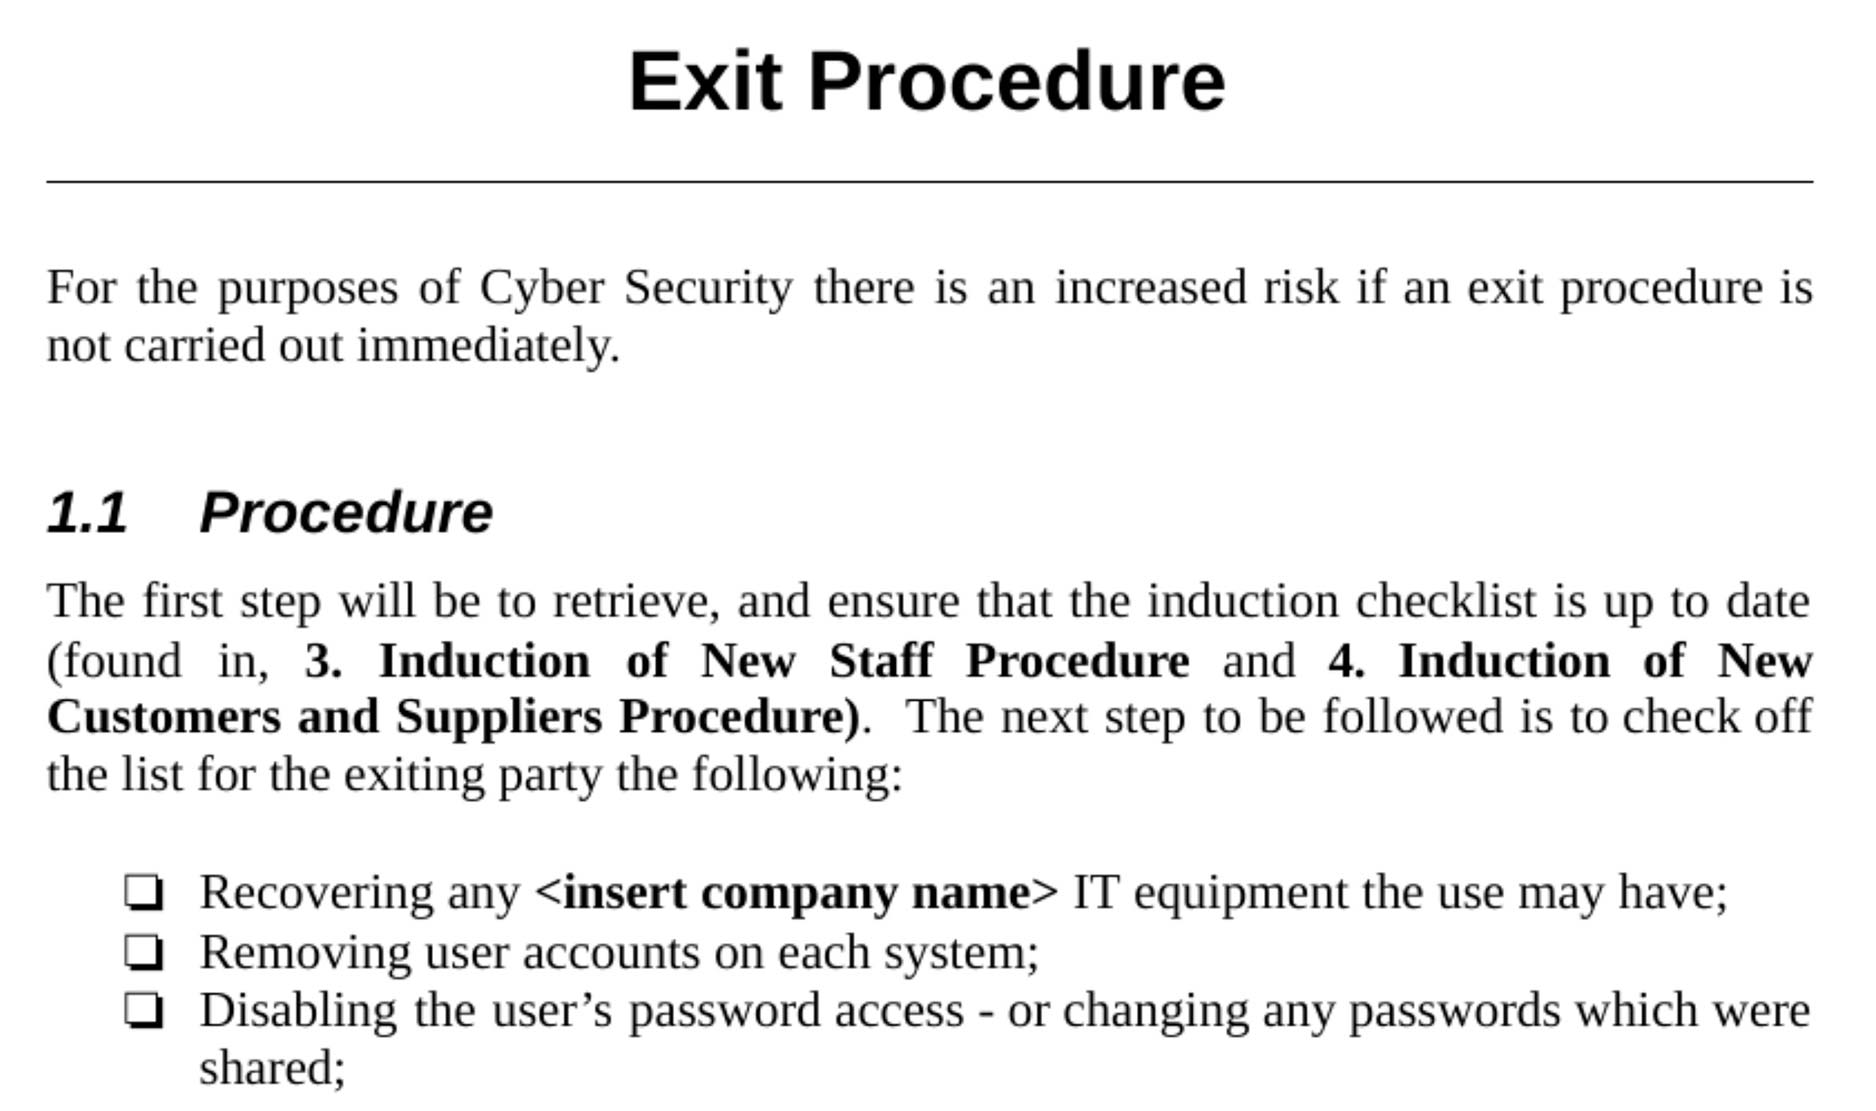
Staff exit process
For the purposes of cyber security there is an increased risk if an exit procedure is not carried out immediately. This policy will provide a structure to mitigate that risk.
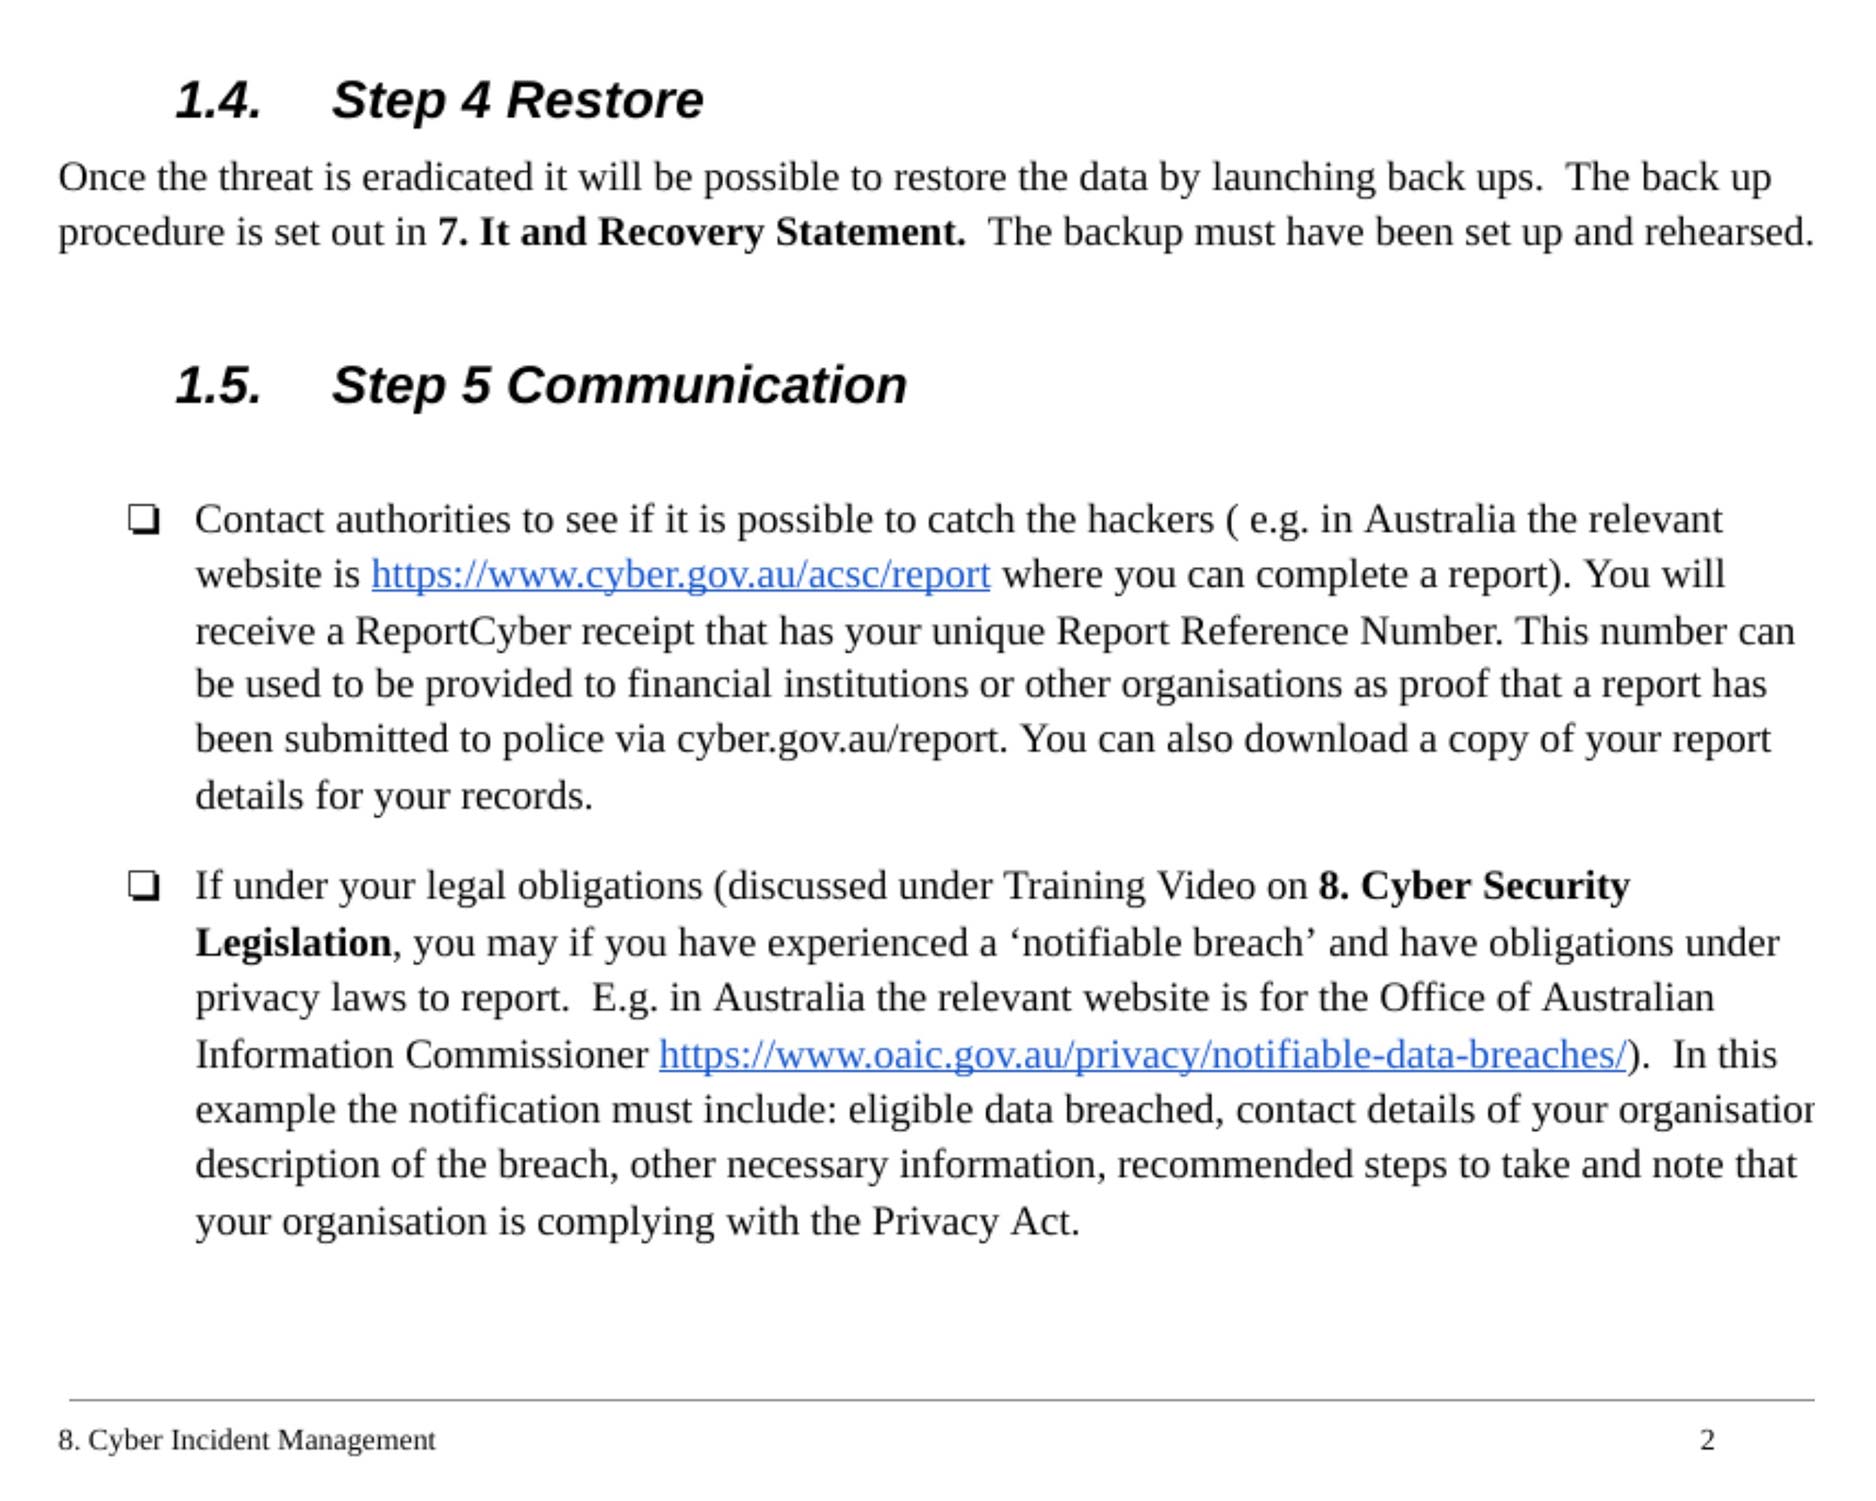
Cyber incident management
This statement is used to manage a Cyber Incident, and develop an actionable incident response plan. This includes having procedures for responding to and managing a cyber attack. It is a key part of cyber risk management for the organisation.
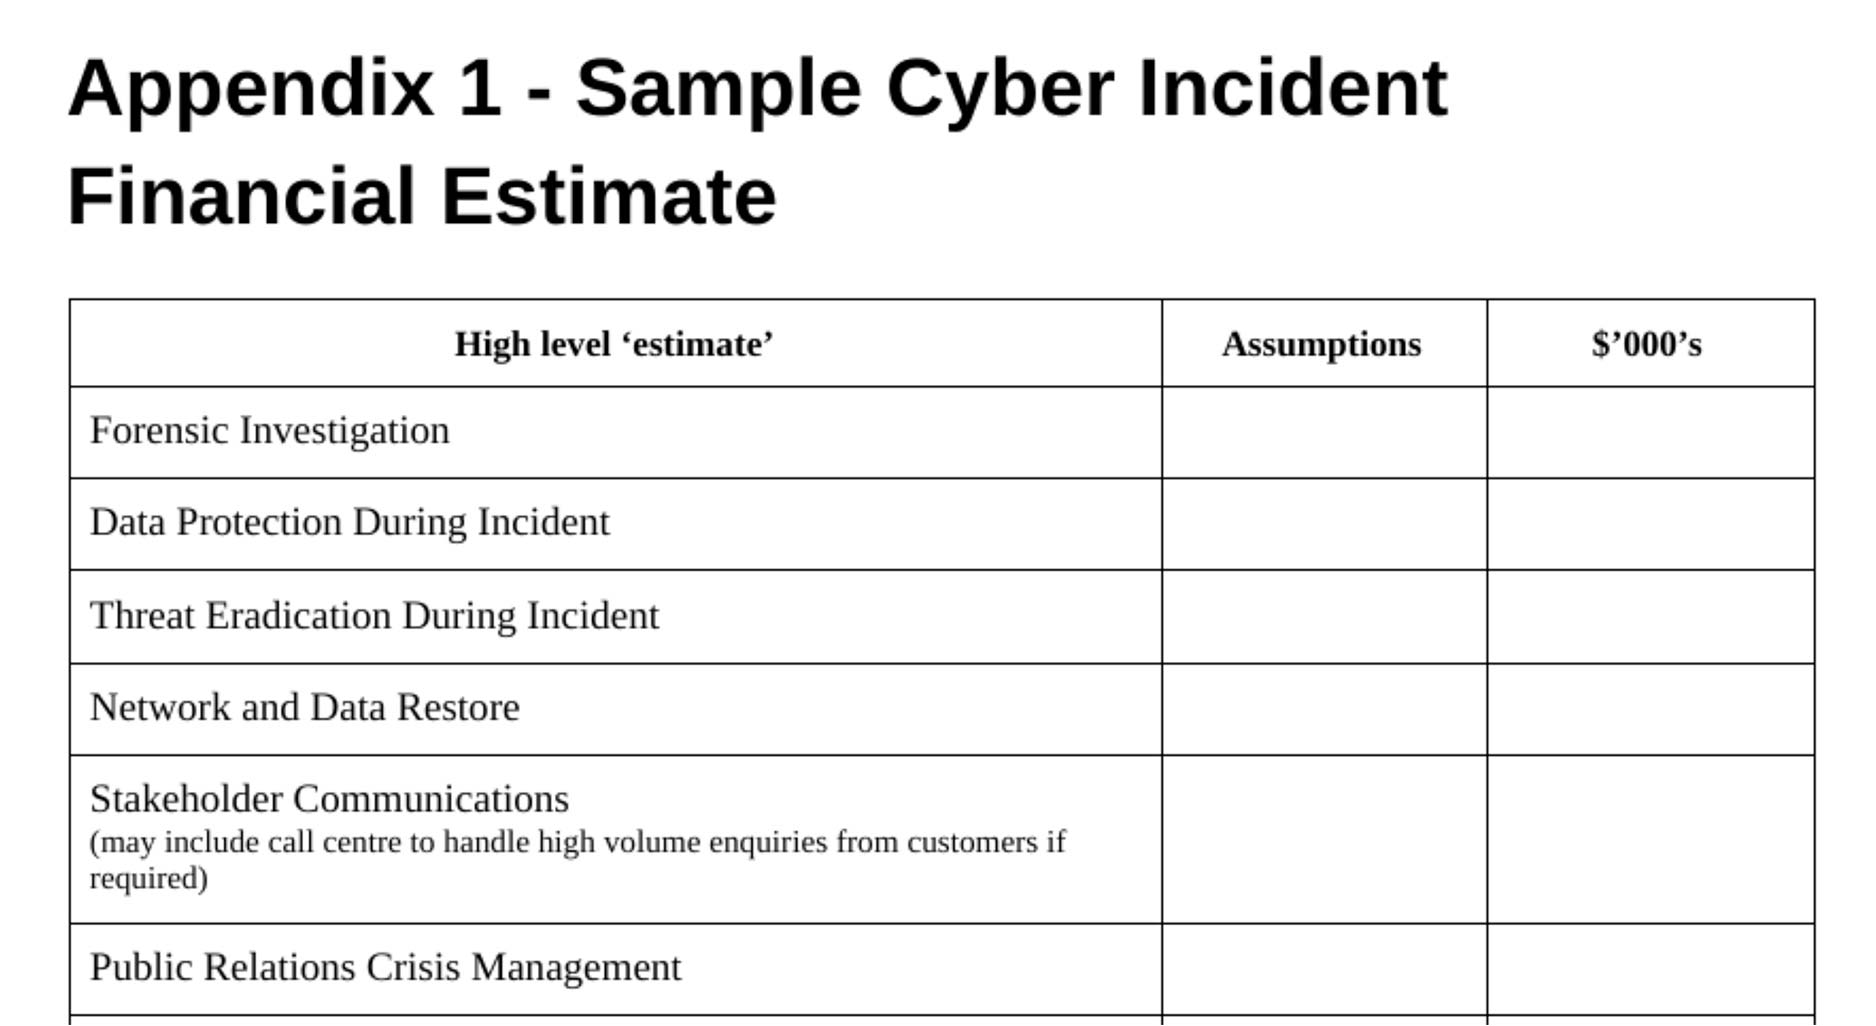
Cyber incident financial estimate
This statement is used to estimate financial risk from a Cyber Incident. An incident can lead to business interruption from computer system downtime, as well as the cost of regulatory investigations and fines. This can lead to a loss of profits, extra expense, and subsequent reputational harm.
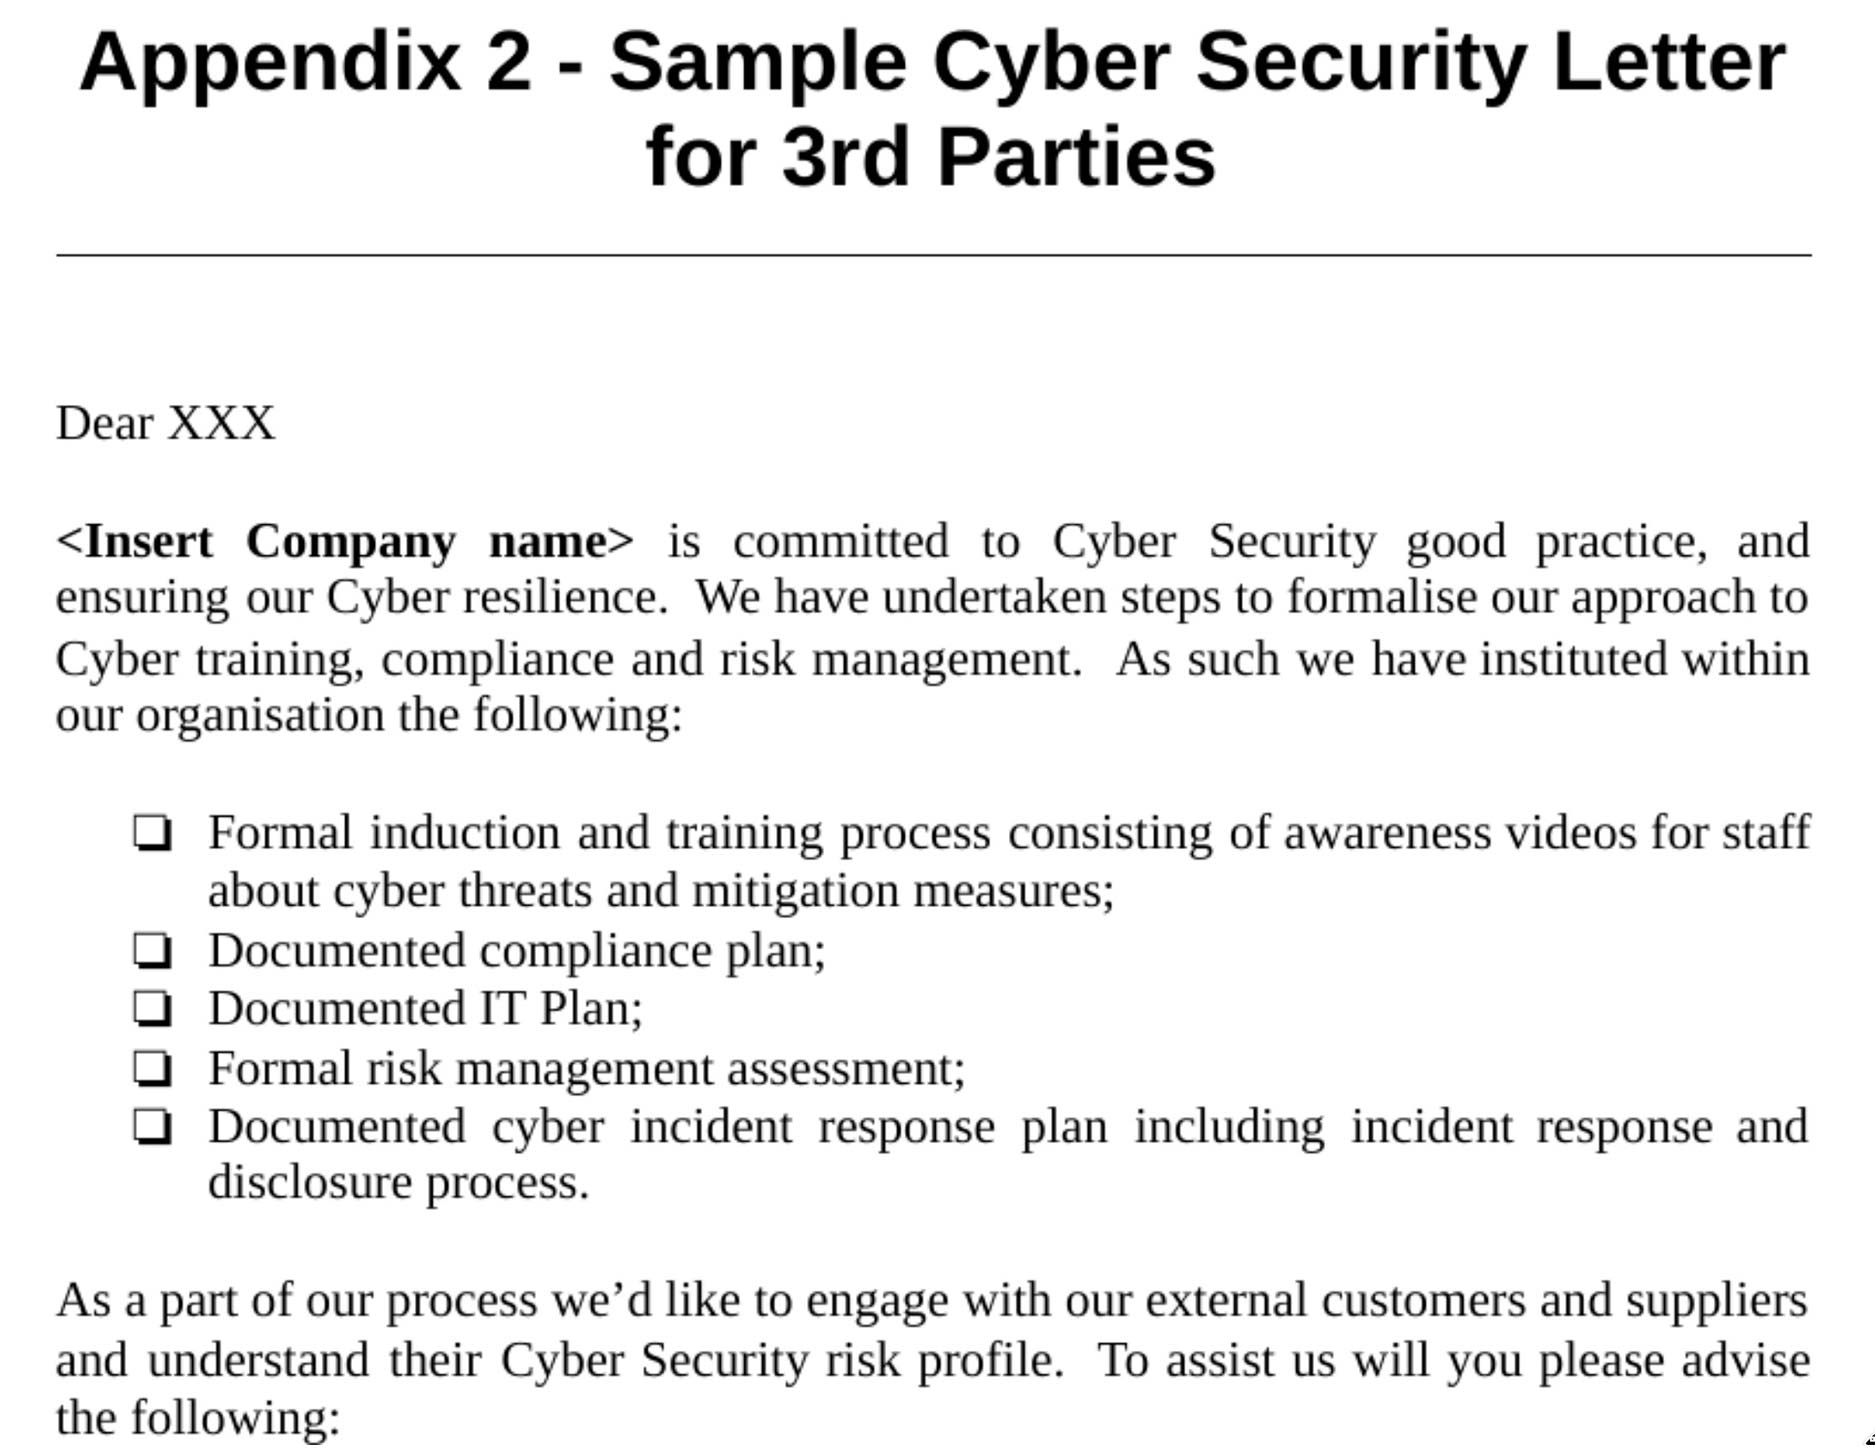
Induction of new customers and suppliers
Where functions are outsourced, processes for the selection and ongoing monitoring of external service providers will include consideration of their cyber security practices at the appointment stage. This allows you to monitor our cyber risk profile through that connection.
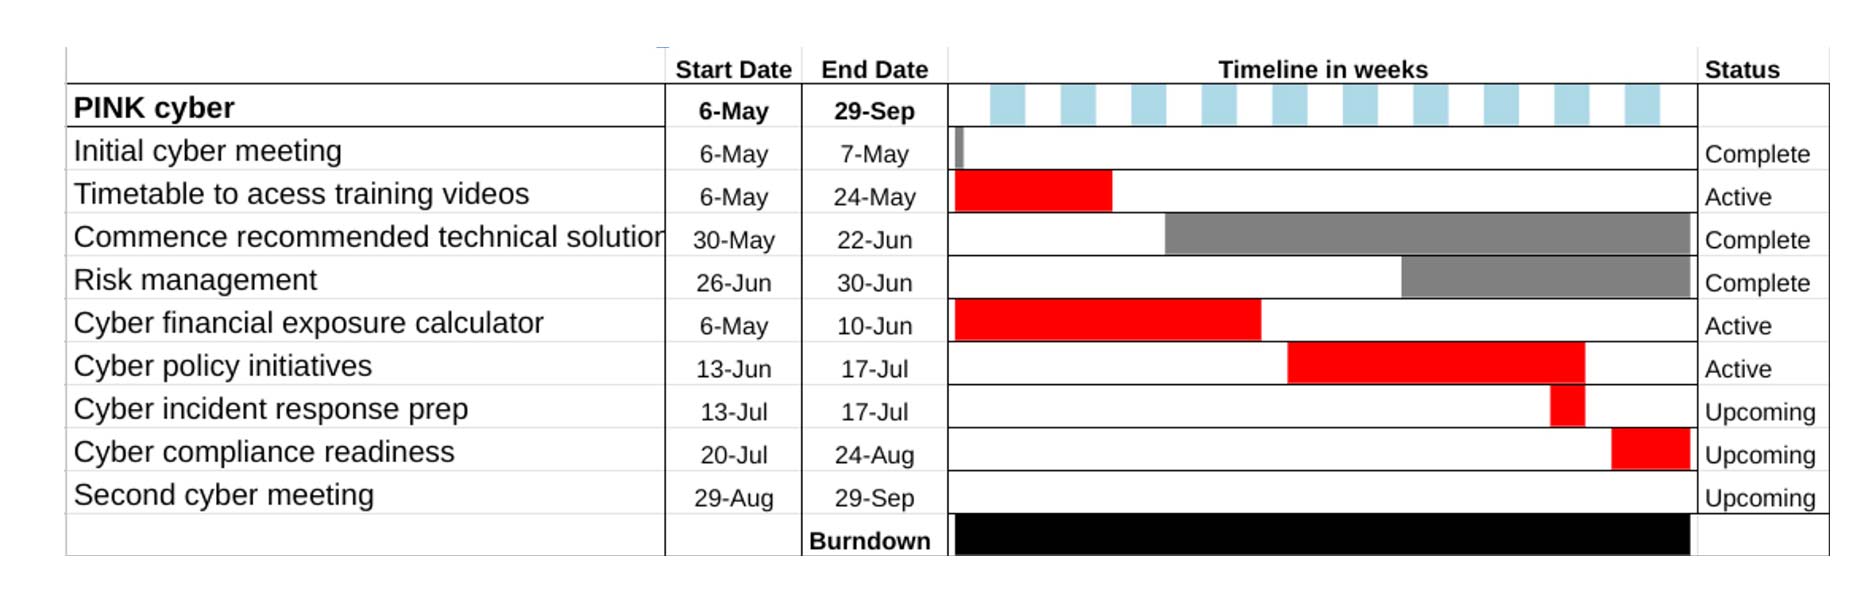
Cyber Tracker
This is a report which allows you to track progress towards your cyber security project at a glance.

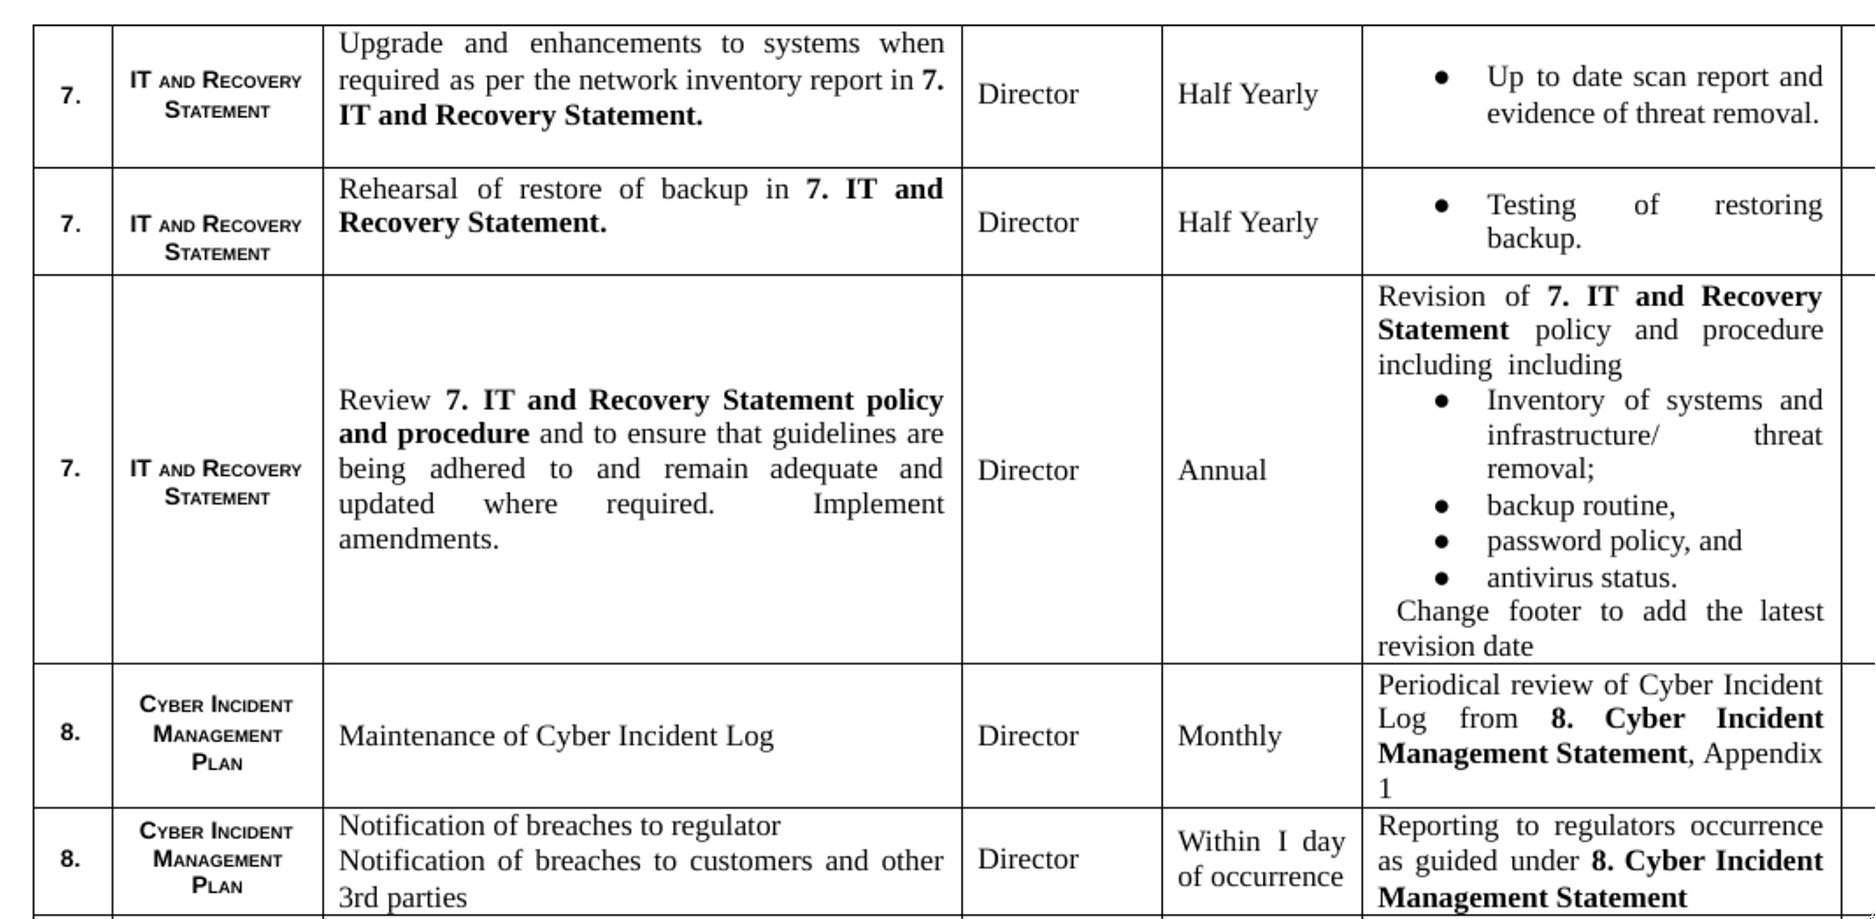
Internal Compliance Plan for Cyber
This Compliance Plan for Cyber provides detail on:
- The Cyber Security measures and procedures in place;
- How compliance with those measures and procedures will be monitored.
Project Plan Outline
Update and prepare a Project Plan Outline for your team to work on implementing good Cyber security practice at your own pace.
Protect Your Business, Your Clients, and Your Reputation


The Compliance Reality
Trust Imperative

The Enterprise Advantage at an SME Cost
You shouldn't have to break the bank just to stay safe. Large corporations spend tens of thousands of dollars on expensive consultants, complex software, and in-house cyber teams. We have stripped away the bloat to give small and mid-sized businesses the key cyber risk management focus points used in enterprise-level protection—built to be deployed in minutes, not months.
CHOOSE THE PERFECT PLAN

Documentation Toolkit
$149
One-time payment.
100% Editable Policies & Procedures
Step-by-Step Implementation Guides
Ready-to-use for corporate records
Instant Audit-Ready Framework
Employee handbook inserts
Training & Awareness Videos Not Included
Most Popular
Complete Cyber Security Bundle
$349
One-time payment.
Everything in the Documentation Toolkit
PLUS: Complete Training & Awareness Videos
HD Video Presentation files (.mp4)
Downloadable files
Training register
Perpetual Corporate License (Single Entity)

❓ Frequently Asked Questions
How does the single-entity license work? Are there any recurring fees?
Can I share these files with my subsidiary companies, contractors, or clients?
What file formats are provided, and can we add our own company branding?
Yes, everything is built to be customised. All policies and procedures are delivered as fully editable Microsoft Word (.docx) files , allowing you to insert your corporate logo, swap company names, and tailor the text in minutes. The training videos are delivered as high-definition MP4 files that play natively on any device.
Where do we host the training videos for our staff?
Wherever your team already communicates. Because you receive the raw MP4 video files, you have total control over hosting. You can drop them directly into your company’s internal Slack channels, Microsoft Teams hubs, a private YouTube or Vimeo link, or upload them to your secure company intranet/Google Drive.
Does this toolkit guarantee compliance with Australian regulatory standards?
This framework was engineered alongside cyber auditors, a former bank CIO, and an insurance underwriter using the proven blueprints of our successful ASX and AFSL kits. It covers the essential, foundational controls required by modern regulatory frameworks and corporate insurance policies to demonstrate active cyber risk management. However, because every business infrastructure is unique, you should adapt the editable policies to match your specific risk profile.
What is your refund policy for digital corporate assets?
Due to the immediate, permanent, and downloadable nature of these digital assets, all sales are final once the checkout is complete and the download links are generated. This policy operates in full compliance with the non-excludable consumer guarantees required under the Australian Consumer Law (ACL) . If you experience any technical issues downloading your ZIP bundles, our Sydney-based support team is here to assist you instantly.